15 - 12 - 2016
| By
Laura Kerrison
Kiwicon 2016 Wrap Up
This November, the Springtimesoft team headed to Kiwicon in Wellington, taking on the earthquake, heavy rain, flooding and road closures to soak up some information with more than 2000 other attendees.
With some time to digest, here are our favourite takeaways from the week…
The highlights:
Out of the Browser into the Fire: Exploiting Native Web-based Applications
This was one of our favourite talks from Kiwicon as this is particularly relevant to the work we’re doing at Springtimesoft. It explored the risks of native clients vs traditional web applications by showing how easy it is to exploit JS inside of desktop apps built with web technologies and create worms or malicious links where the user doesn’t even realise that something malicious just happened in the background.
View the presentation info.
Luring developers with candy and other evil tricks
Eleanor Saitta’s (@dymaxion) talk on the way Etsy approaches security was enlightening. It covered lowering or removing the barriers between developer and security teams and having them work together more closely and the importance of making it okay to ask questions and not feel shy about bringing up potential security hazards. Also, Eleanor emphasised the need to really understand your products at a human level and make decisions based on humans! In terms of security, this means understanding who your attackers are and their motivations.
Eleanor has spent the past decade formulating these ideas and that was very evident in her presentation.
View the presentation info.
Defending the Gibson in the Age of Enlightenment
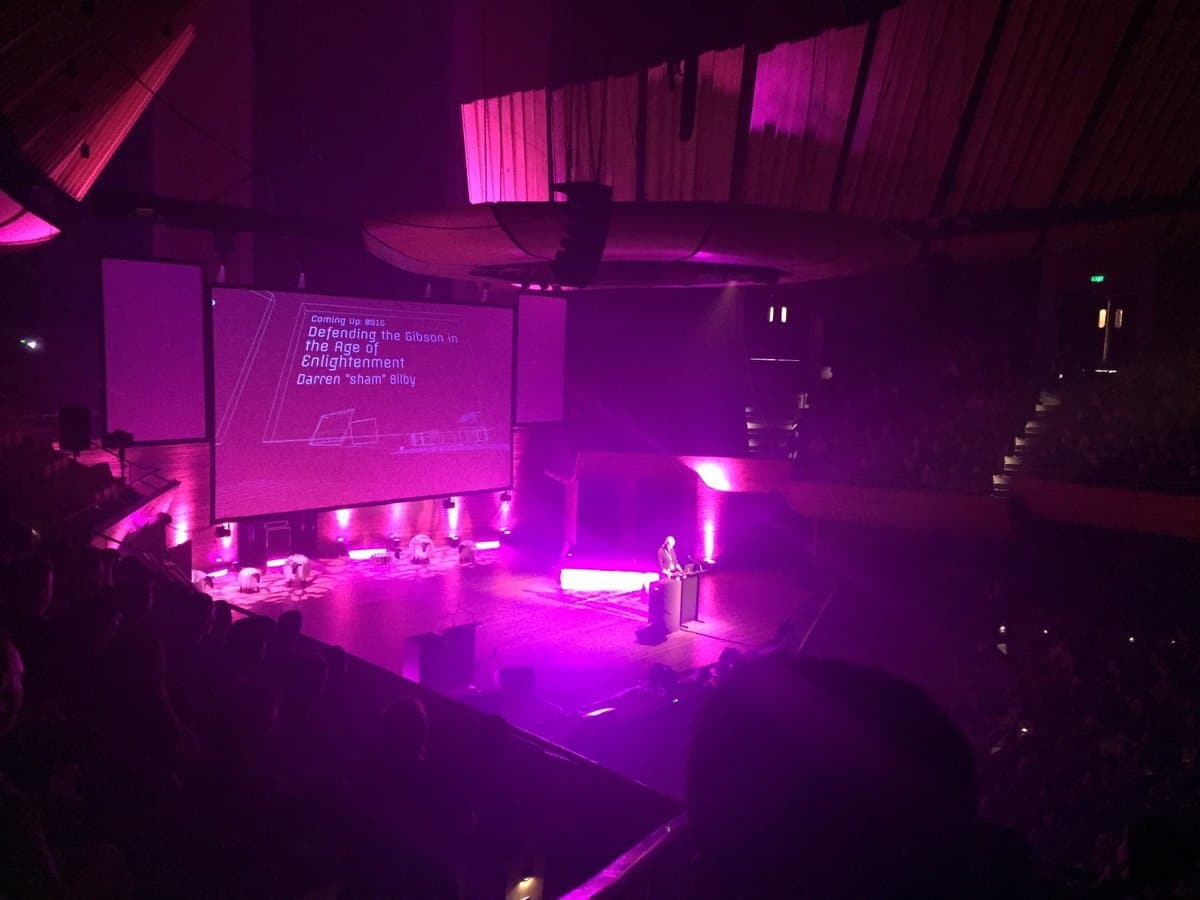
Keynote from Darren Bilby of Google - discussing some of the security strategies and implementations by Google over the past decade, and forecasting technologies to protect infrastructure in the future.
Radiation-induced cryptographic failures and how to defend against them
Peter Gutmann returned for his 10th year of Kiwicon with as crazy a talk as usual. This discussion explored the effects of radiation on computer security mechanisms (and computers in general), and how to protect against this. Not to mention having radioactive material on stage during the talk to keep things interesting!
Our top takeaways
Davi Ottenheimer’s talk on the flaws of machine learning and AI
Zane - “I took a lot away from Davi’s machine learning talk, in particular putting a lot of extra thought into the training data that is used for such projects to avoid bias as much as possible.”
NodeJS: Remote Code Execution as a Service talk
The need to be cautious about where NodeJS is being used in our stack due to a lack of signatures, and version pinning, making way for malicious library updates.
_blank slate
Don’t use target="_blank" without rel="noopener noreferrer". You can read more about this on Jitbit.
This was a practical takeaway from Jen’s talk “_blank slate” – a short but interesting talk about the exploit of target="_blank" via JS. These mitigations are to be considered when developing applications that allow users to submit links which are then later opened in a new window.
A few more memorable moments
- A throat singing performance in the middle of the con was pretty rad: https://www.youtube.com/watch?v=4N0Uszo87xA
- @Amm0nRa giving the middle finger to censorship and releasing the HID iClass master key during his presentation.
- PHP Internals: Exploit Dev Edition https://2016.kiwicon.org/the-con/talks/#e258
- @metlstorm, one of the best MC’s we’ve seen. Especially when stopping the show to call someone out for unsuitable behaviour.
- Great water bottles
Thanks Kiwicon Crüe!
Kiwicon was the perfect mix of security, research and development talks from a variety of perspectives.
We hope that this sparks a rise of more security focussed talks amongst NZ conferences and we eagerly await the return of Kiwicon - there will never be anything quite like it :)
Tags
- conferences
- Wellington
- Security